Vulnerability · Published Sep 15, 2026 · Assigned by VulDB
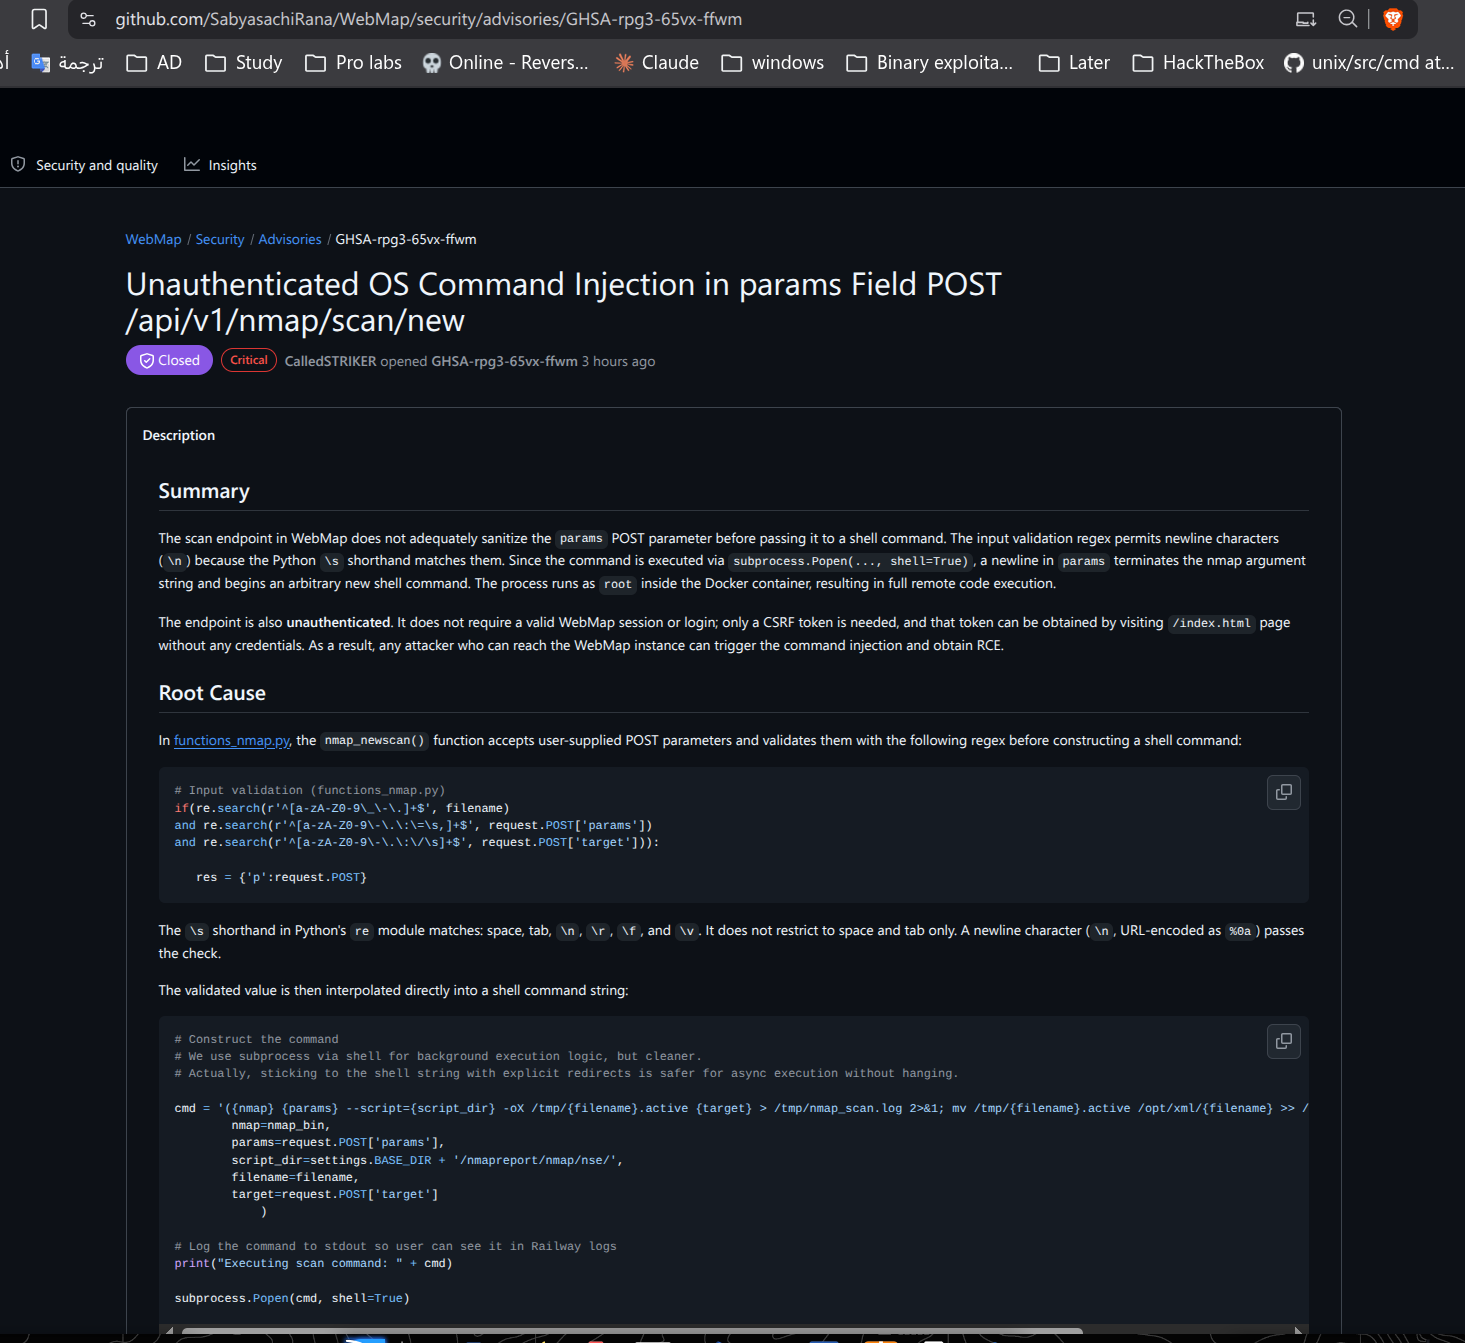
CVE-2026-90843SabyasachiRana WebMap New Nmap Scan functions_nmap.py nmap_newscan os command injection
High 8.3
In plain English
A high-severity OS command injection in WebMap from SabyasachiRana. Proof-of-concept exploit code is public. The chance it is exploited in the next 30 days is estimated at 2.2% (higher than 82% of all known vulnerabilities).
Official description
A security vulnerability has been detected in SabyasachiRana WebMap up to 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25. This affects the function nmap_newscan of the file functions_nmap.py of the component New Nmap Scan Handler. Such manipulation of the argument target/params leads to os command injection. The attack may be launched remotely. The exploit has been disclosed publicly and may be used. The name of the patch is 3d52f65803a2716bff14d938352c6fef45b0cfb6. A patch should be applied to remediate this issue. This issue got fixed with a silent patch.
Affected products (as reported)
| Vendor | Product | Versions |
|---|---|---|
| SabyasachiRana | WebMap | 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25 |
Weakness: CWE-78, CWE-77 · Vector: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:L/I:L/A:L/E:P/RL:O/RC:C
References
- VDB-403395 | SabyasachiRana WebMap New Nmap Scan functions_nmap.py nmap_newscan os command injection vdb-entry, technical-description
- VDB-403395 | CTI Indicators (IOB, IOC, TTP, IOA) signature, permissions-required
- CVE-2026-90843 | CVE Analysis and Report third-party-advisory
- Submit #925586 | WebMap 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25 (CWE-78,CWE-306): OS Command Injection + Missing Authentication third-party-advisory
- https://calledstriker.gitbook.io/blog/security-research/webmap exploit
- https://raw.githubusercontent.com/CalledSTRIKER/CalledSTRIKER-gitbook/refs/heads/main/security-research/2026-05-30_12-29.png related
- https://github.com/SabyasachiRana/WebMap/commit/3d52f65803a2716bff14d938352c6fef45b0cfb6 broken-link, patch
- https://github.com/SabyasachiRana/WebMap/ broken-link, product