Vulnerability · Published May 11, 2026 · Assigned by VulDB
CVE-2026-8255Devs Palace ERP Online add_new_customer cross site scripting
Low 2.4
In plain English
A low-severity cross-site scripting in ERP Online from Devs Palace. Proof-of-concept exploit code is public. The chance it is exploited in the next 30 days is estimated at 0.2% (higher than 10% of all known vulnerabilities).
Official description
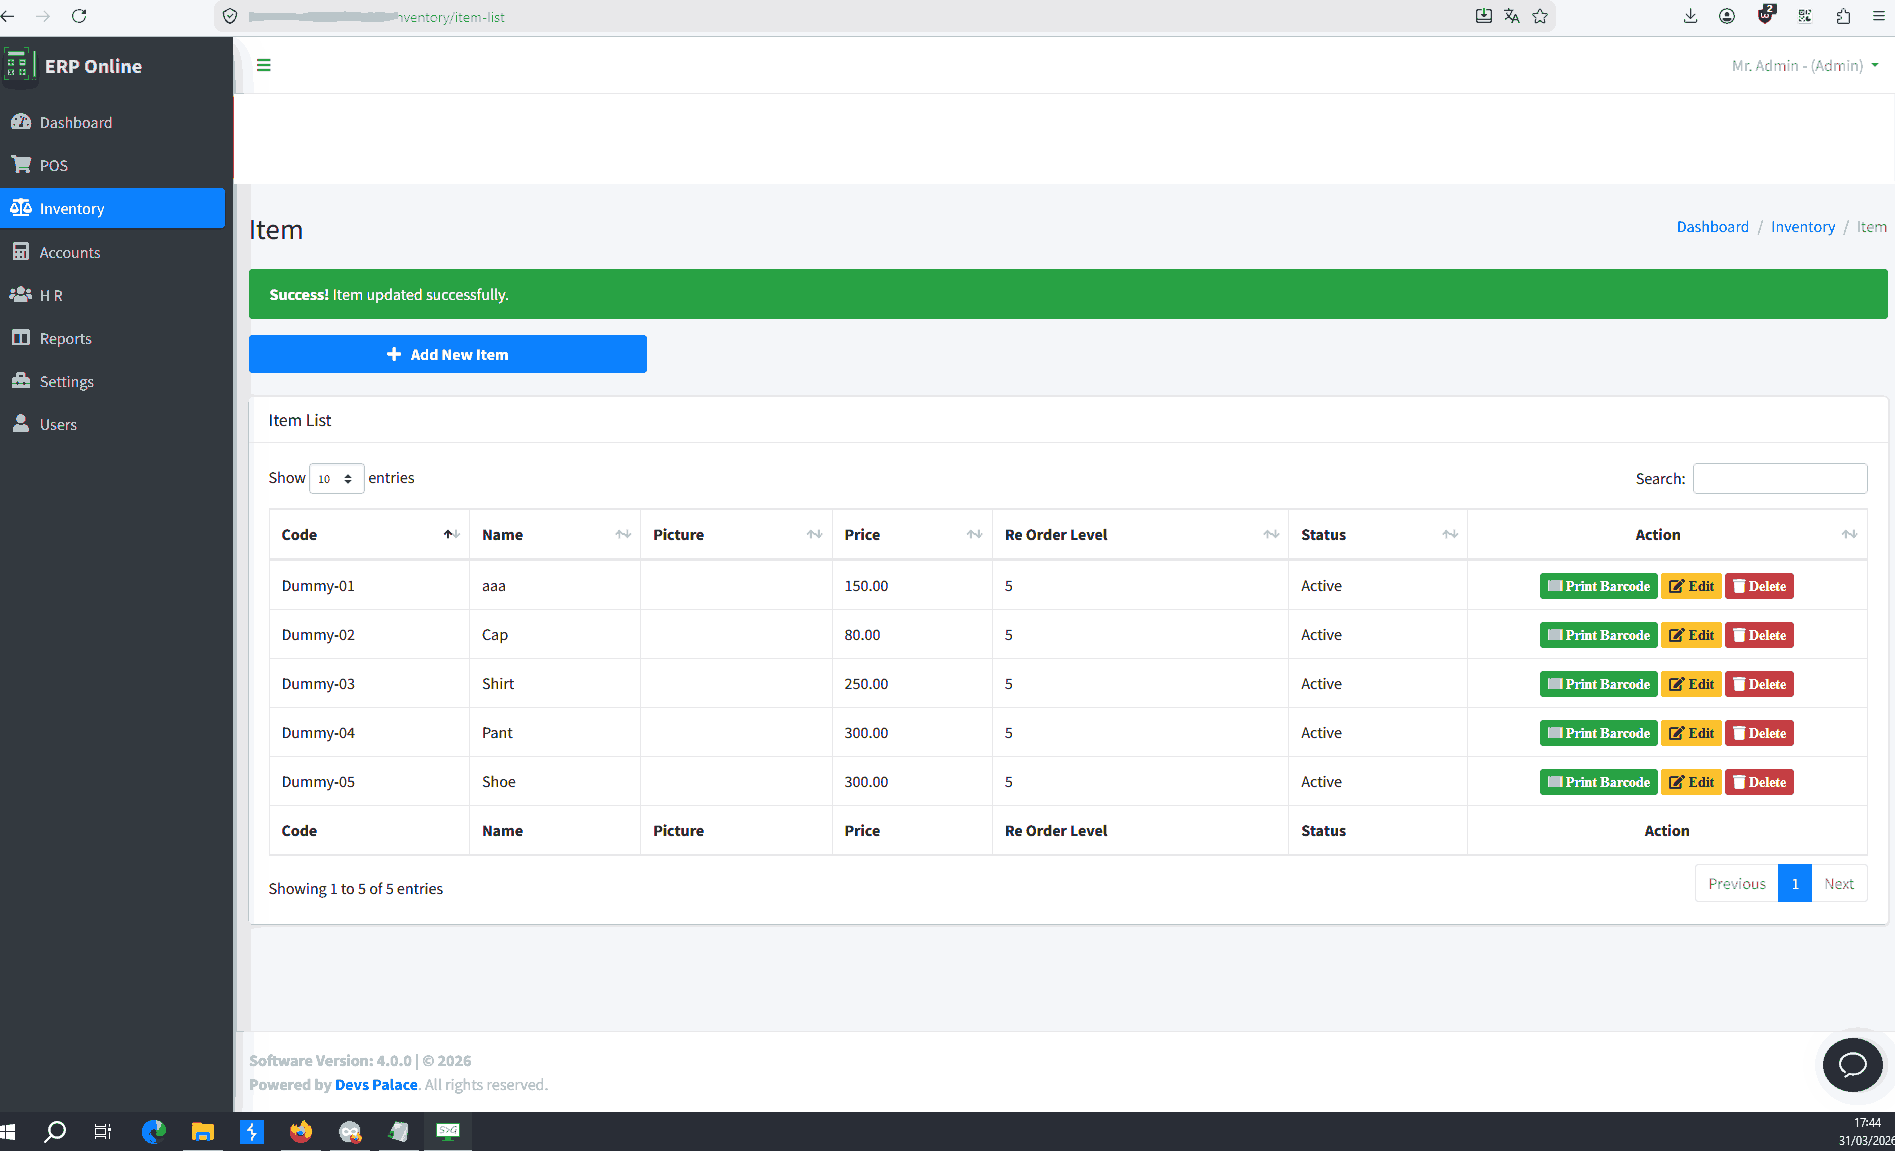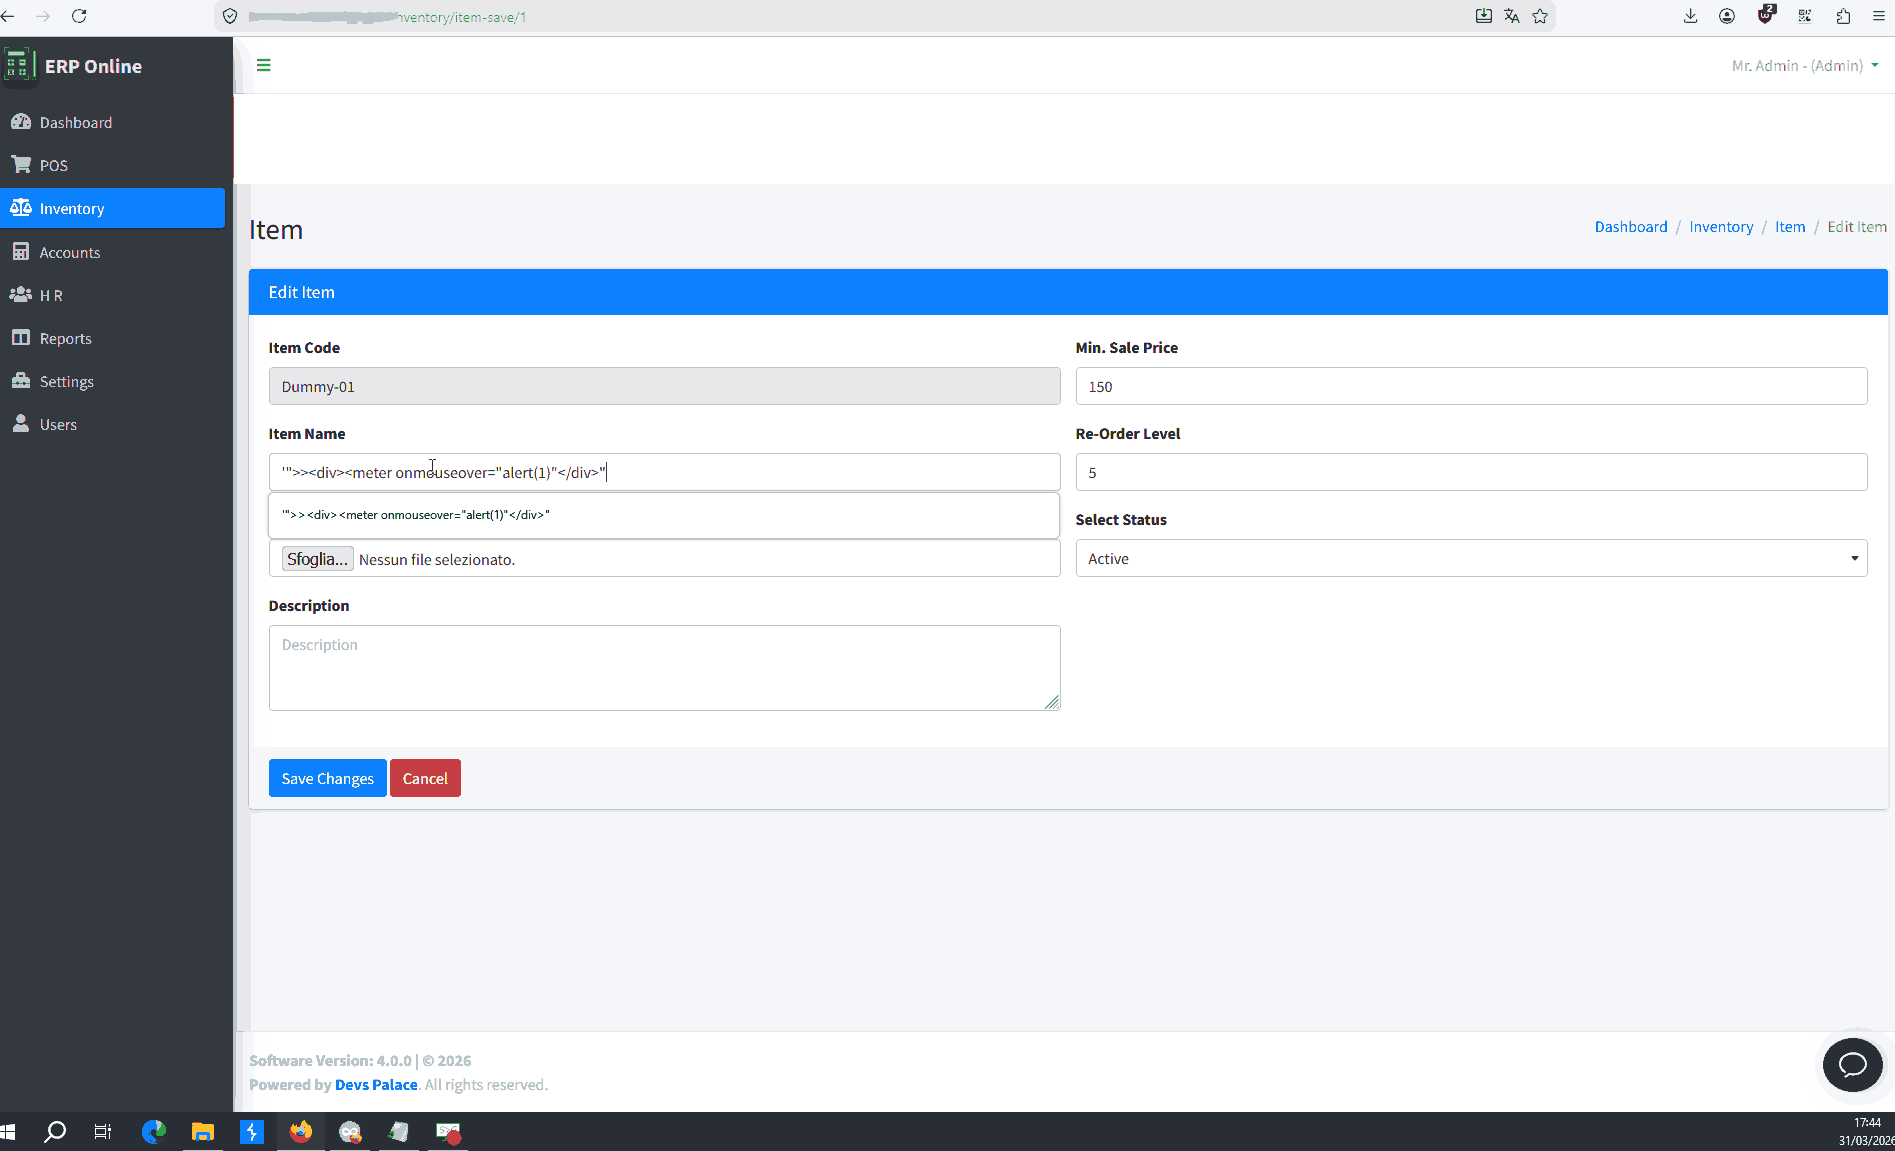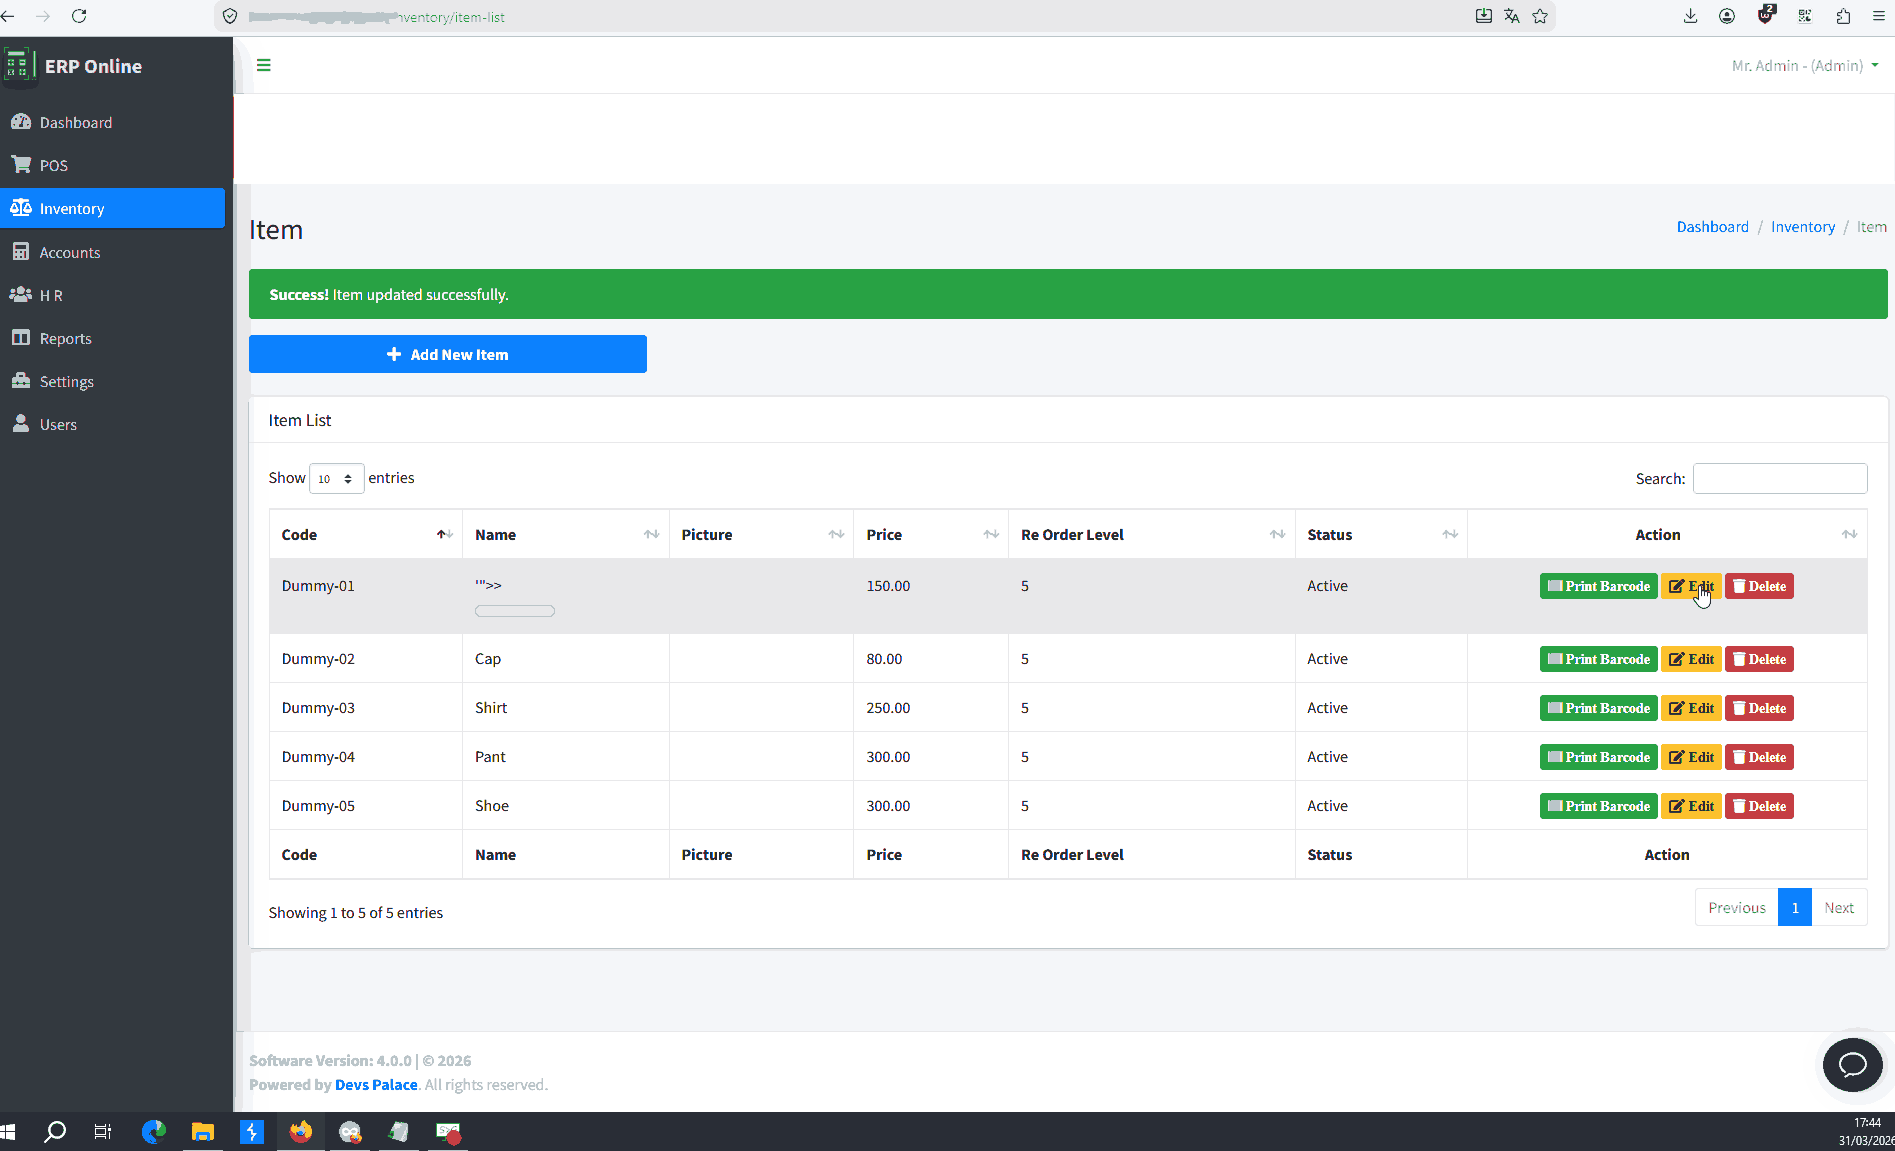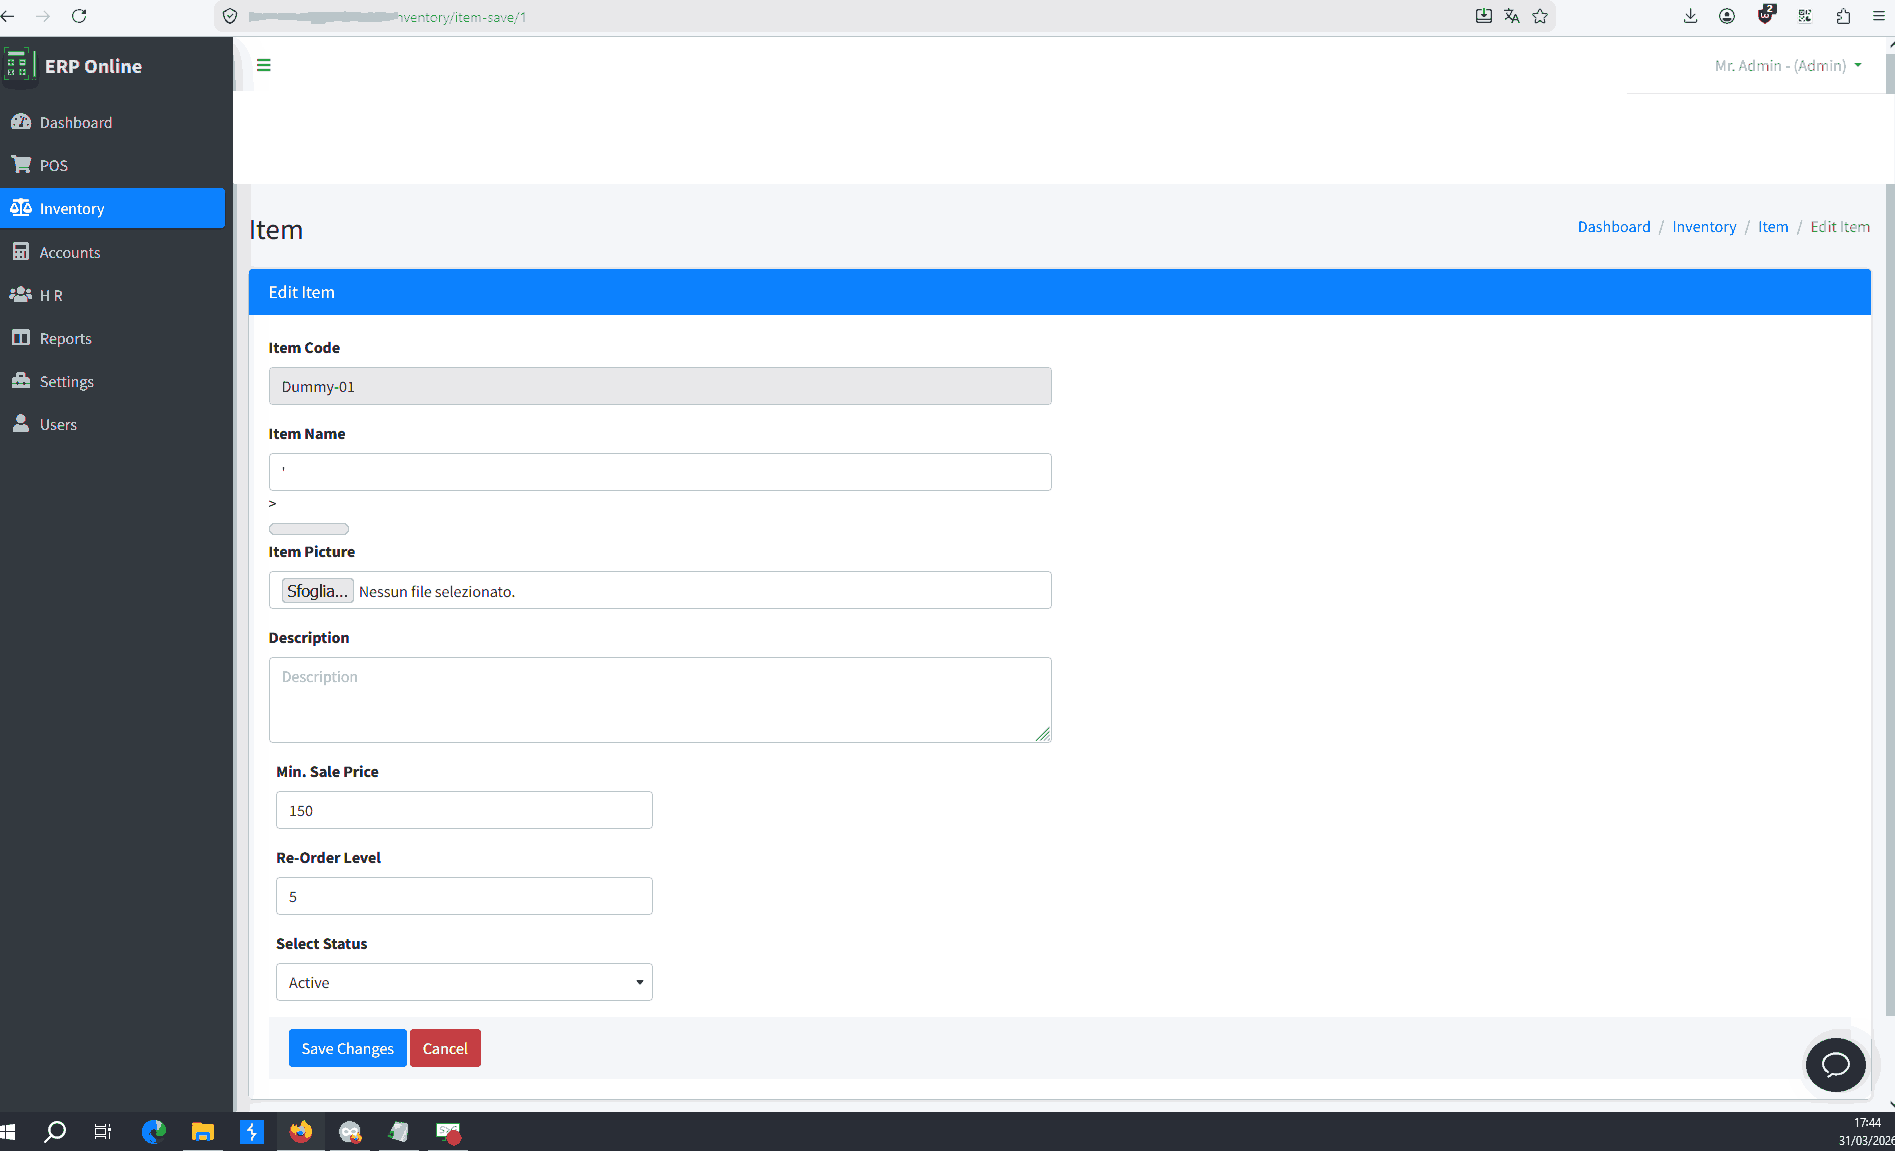
A weakness has been identified in Devs Palace ERP Online up to 4.0.0. This affects an unknown part of the file /inventory/add_new_customer. This manipulation causes cross site scripting. The attack can be initiated remotely. The exploit has been made available to the public and could be used for attacks. The vendor was contacted early about this disclosure but did not respond in any way.
Affected products (as reported)
| Vendor | Product | Versions |
|---|---|---|
| Devs Palace | ERP Online | 4.0 |
Weakness: CWE-79, CWE-94 · Vector: CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:N/I:L/A:N/E:P/RL:X/RC:R
References
- VDB-362552 | Devs Palace ERP Online add_new_customer cross site scripting vdb-entry
- VDB-362552 | CTI Indicators (IOB, IOC, TTP, IOA) signature, permissions-required
- Submit #808526 | Devs Palace ERP Online 4.0.0 Code Injection third-party-advisory
- https://olografix.org/acme/_poc/ERP_Online-POC1.gif exploit