Vulnerability · Published Nov 2, 2021 · Assigned by mitre
CVE-2020-23754
Critical 9.6
In plain English
A critical-severity security flaw in the affected software. There are no confirmed reports of exploitation so far. The chance it is exploited in the next 30 days is estimated at 1.6% (higher than 76% of all known vulnerabilities).
Severity (CVSS NVD)9.6Critical
Exploit odds (30 days)1.6%top 24.1% of all CVEs
Exploited in the wildNo reportsnot in CISA KEV
Attack toolingNoneno public tooling known
Official description
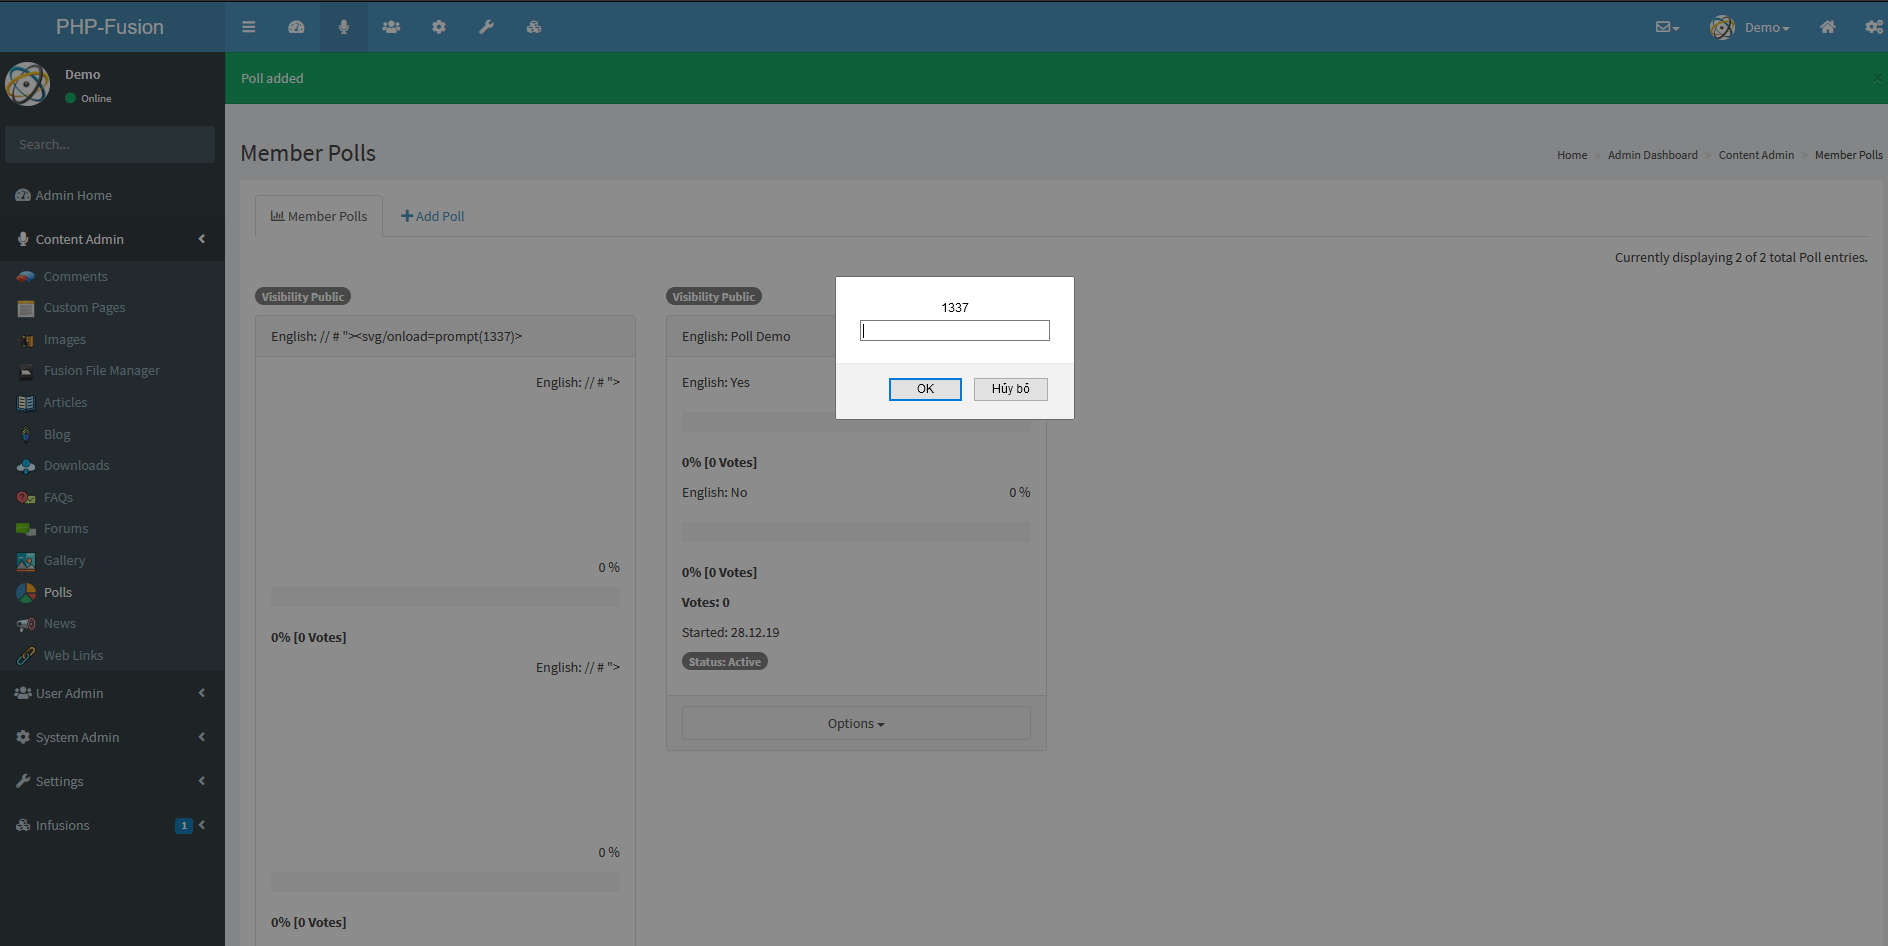
Cross Site Scripting (XSS) vulnerability in infusions/member_poll_panel/poll_admin.php in PHP-Fusion 9.03.50, allows attackers to execute arbitrary code, via the polls feature.
Affected products (as reported)
References
- https://github.com/php-fusion/PHP-Fusion/issues/2315 x_refsource_MISC
- https://user-images.githubusercontent.com/62001260/81574112-9412e100-93cf-11ea-9493-615a70162034.PNG x_refsource_MISC
- https://user-images.githubusercontent.com/62001260/81574006-6fb70480-93cf-11ea-814c-55a96d2fe95e.PNG x_refsource_MISC