Vulnerability · Published Apr 21, 2026 · Assigned by VulDB
CVE-2026-6743WebSystems WebTOTUM Calendar cross site scripting
Low 3.5
In plain English
A low-severity cross-site scripting in WebTOTUM from WebSystems. Proof-of-concept exploit code is public. The chance it is exploited in the next 30 days is estimated at 0.2% (higher than 9% of all known vulnerabilities).
Official description
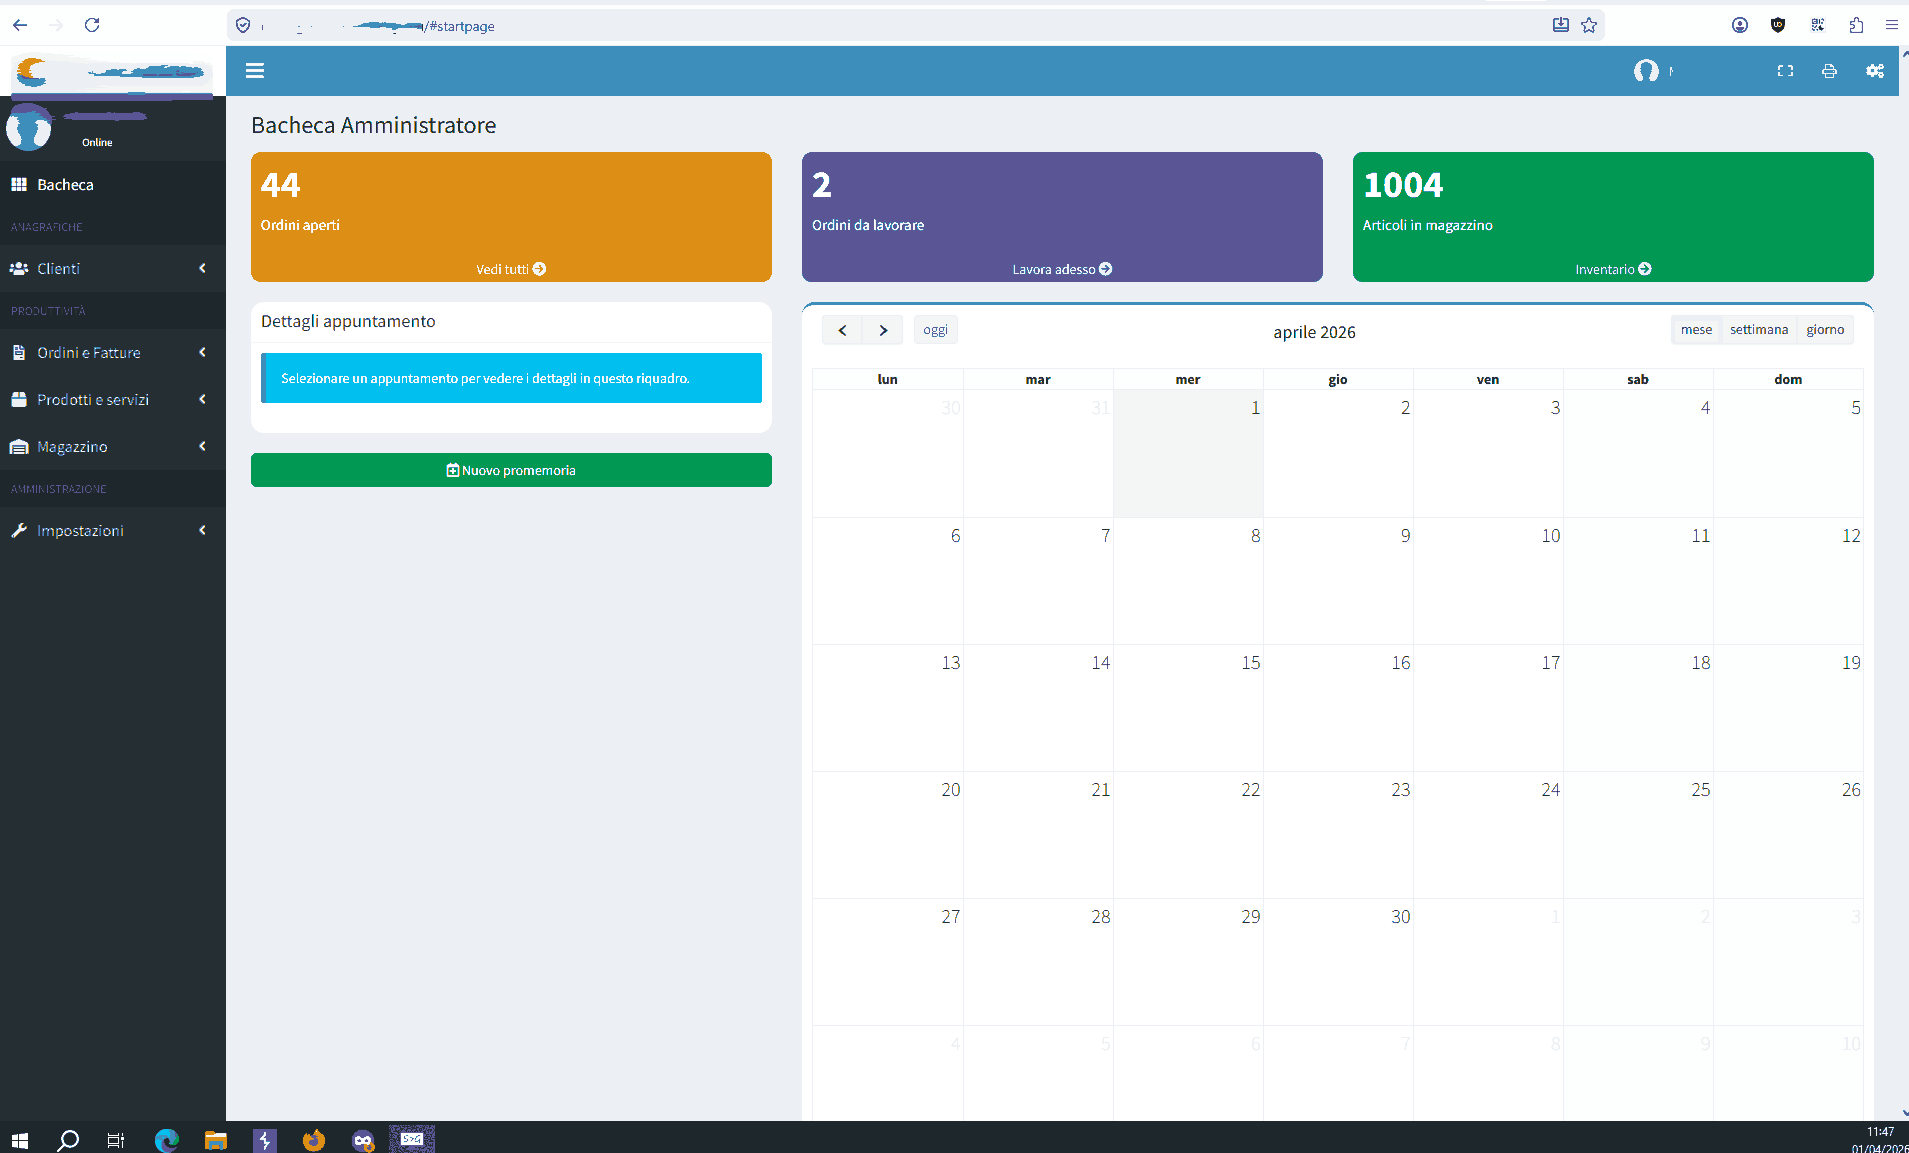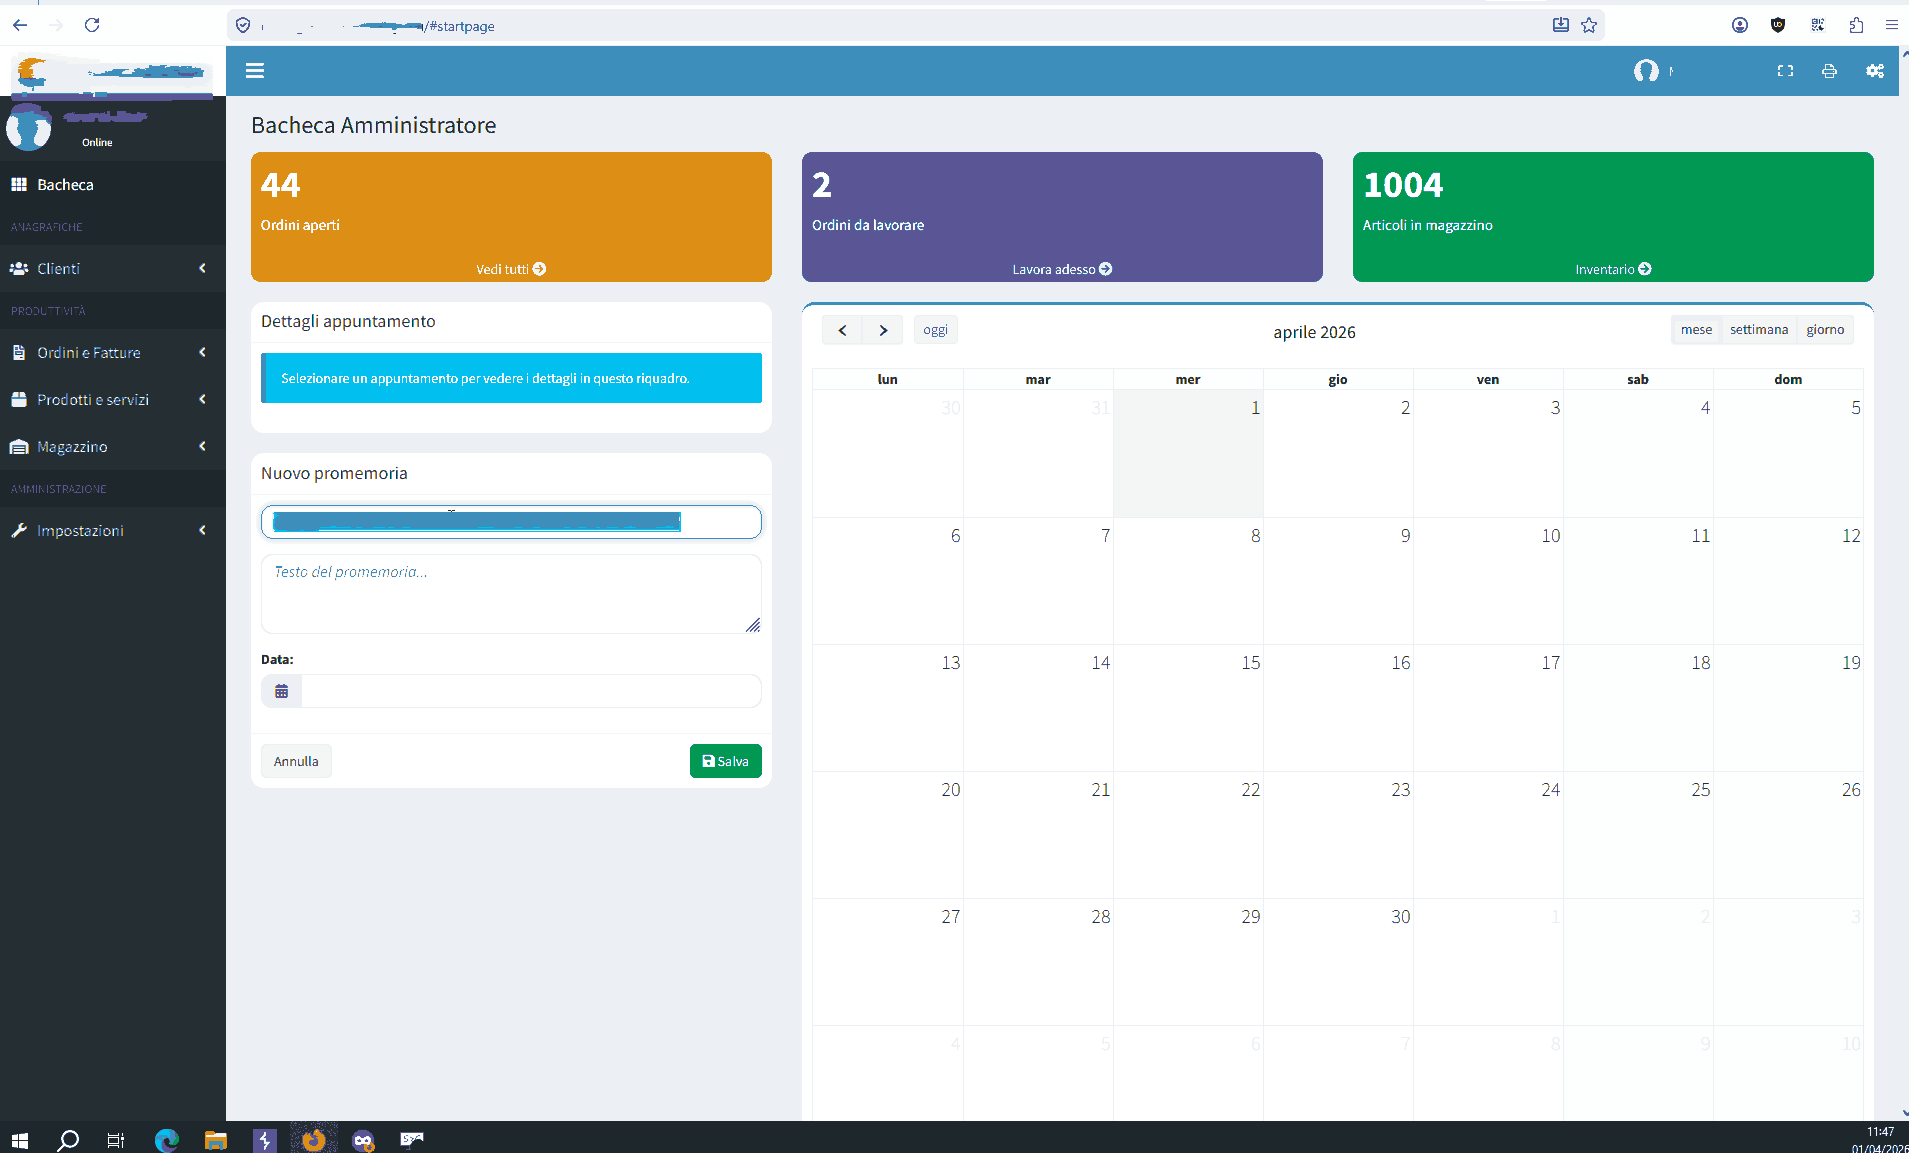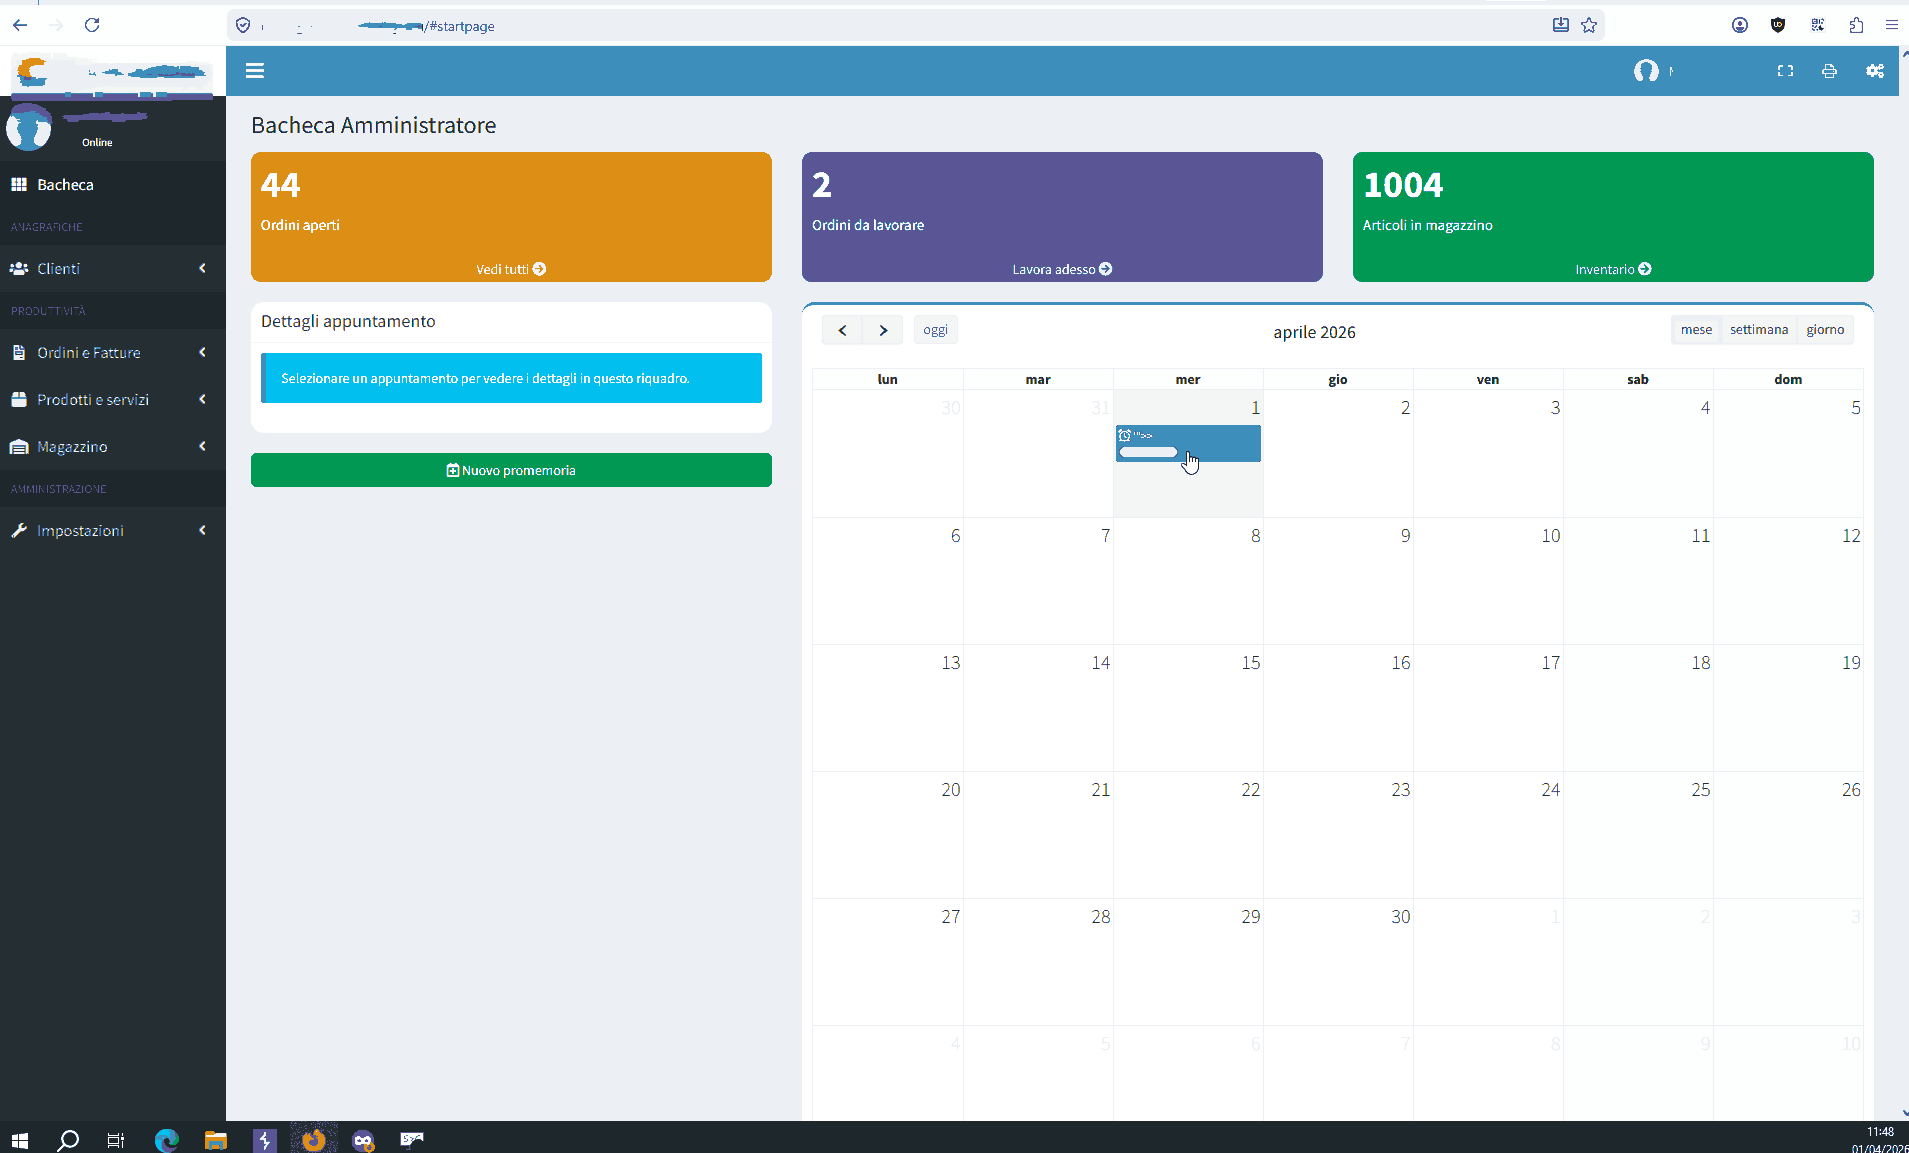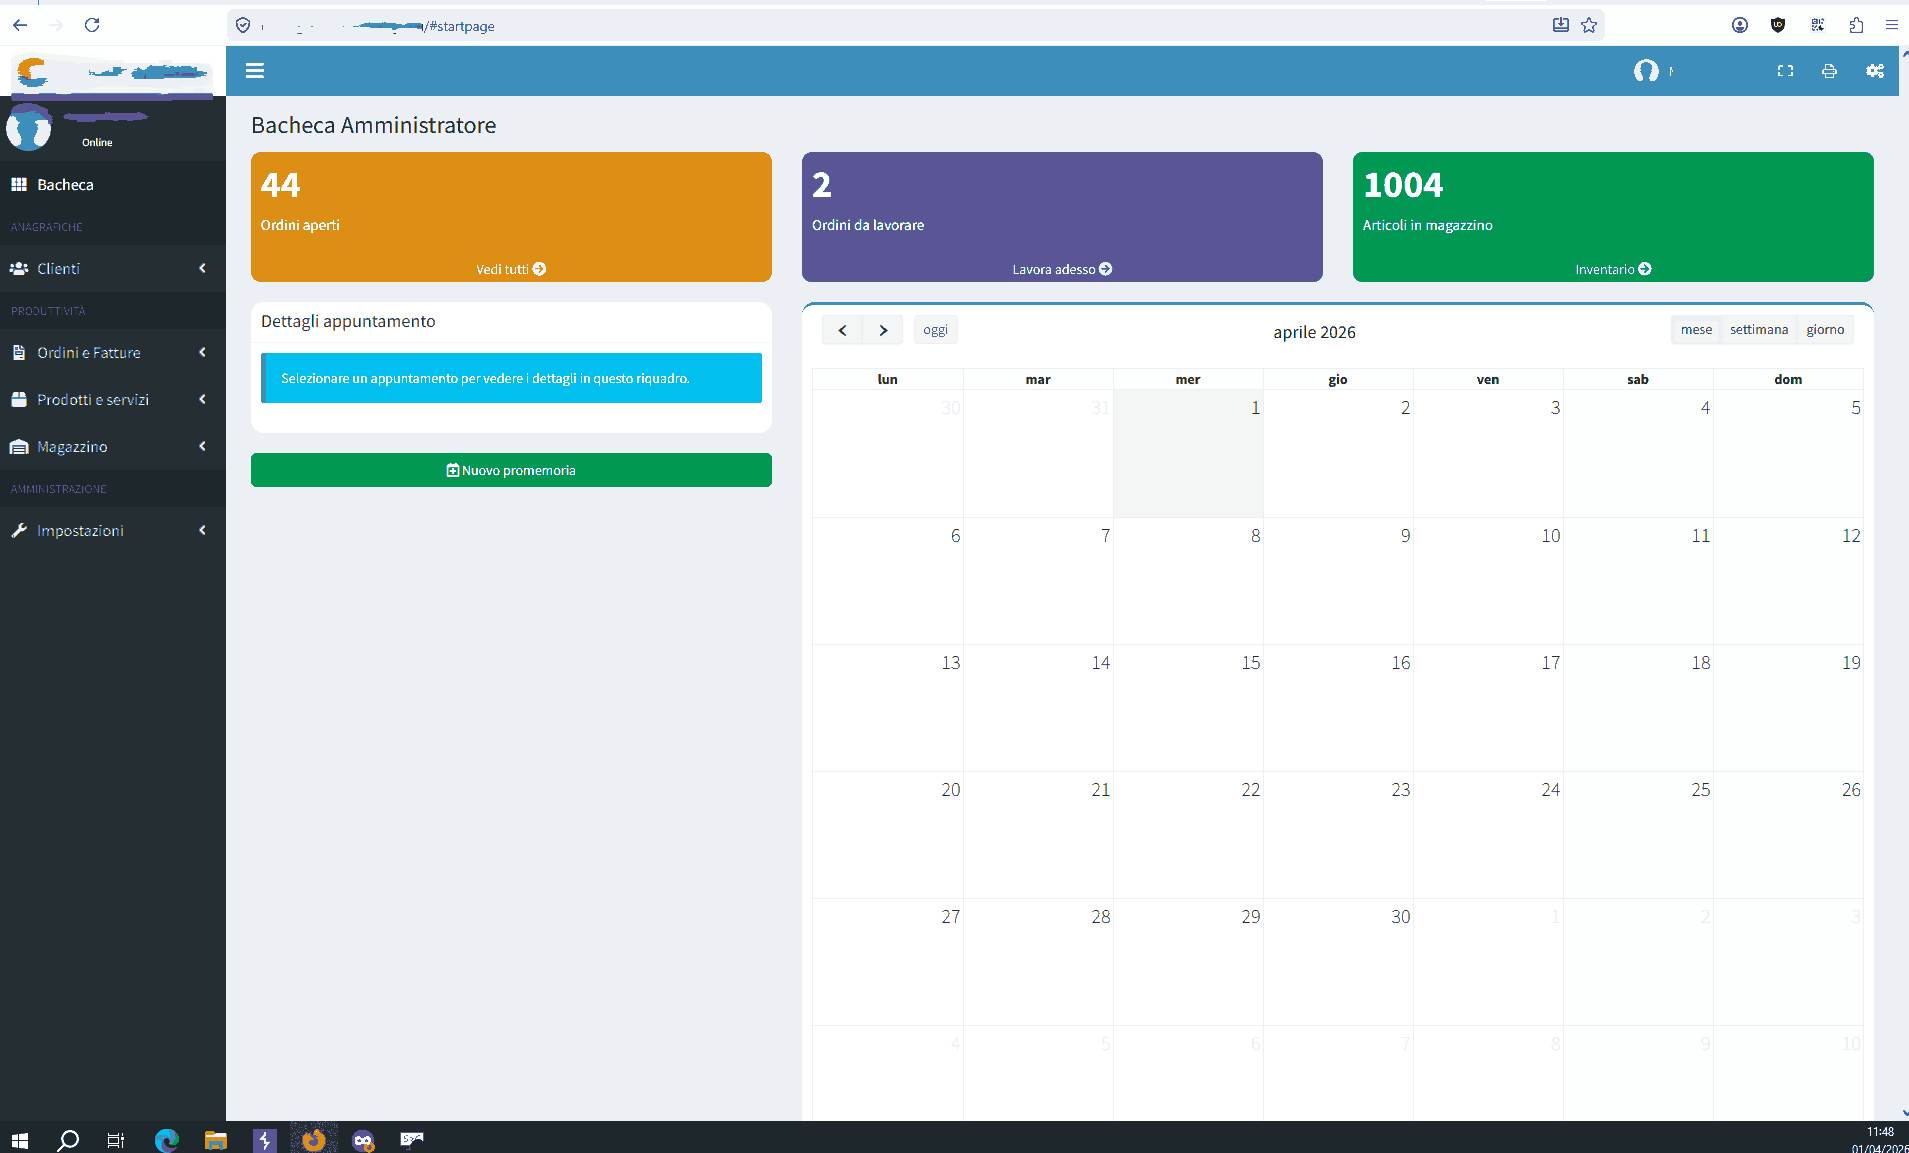
A vulnerability has been found in WebSystems WebTOTUM 2026. This impacts an unknown function of the component Calendar. The manipulation leads to cross site scripting. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. Upgrading the affected component is recommended. The vendor was contacted early, responded in a very professional manner and quickly released a fixed version of the affected product.
Affected products (as reported)
| Vendor | Product | Versions |
|---|---|---|
| WebSystems | WebTOTUM | 2026 |
Weakness: CWE-79, CWE-94 · Vector: CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:L/A:N/E:P/RL:O/RC:C
References
- VDB-358434 | WebSystems WebTOTUM Calendar cross site scripting vdb-entry
- VDB-358434 | CTI Indicators (IOB, IOC, TTP) signature, permissions-required
- Submit #794617 | WebSystems WebTOTUM (2026) Cross Site Scripting third-party-advisory
- https://olografix.org/acme/WebTOTUM-POC.gif exploit
- https://www.websys.eu/gestionale-online-in-cloud-per-pmi-callcenter patch