Vulnerability · Published Sep 4, 2022 · Assigned by VulDB
CVE-2022-3118Sourcecodehero ERP System Project processlogin.php sql injection
High 7.3
In plain English
A high-severity SQL injection in ERP System Project from Sourcecodehero. Proof-of-concept exploit code is public. The chance it is exploited in the next 30 days is estimated at 0.9% (higher than 59% of all known vulnerabilities).
Official description
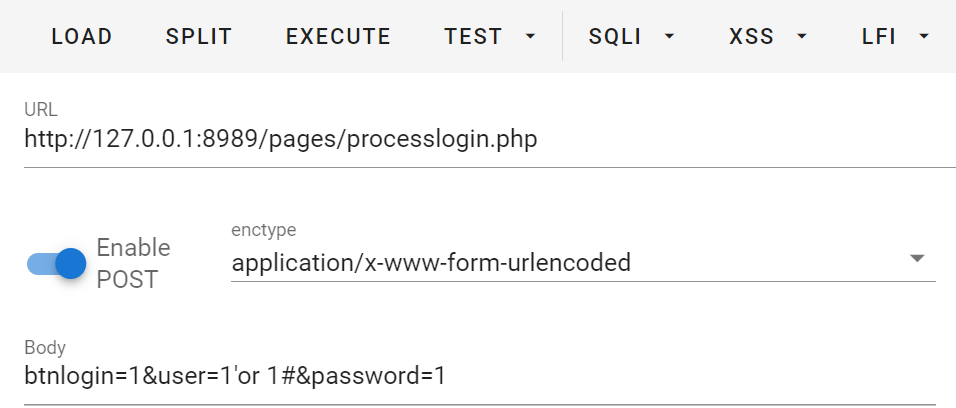
A vulnerability was found in Sourcecodehero ERP System Project. It has been rated as critical. This issue affects some unknown processing of the file /pages/processlogin.php. The manipulation of the argument user leads to sql injection. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-207845 was assigned to this vulnerability.
Affected products (as reported)
| Vendor | Product | Versions |
|---|---|---|
| Sourcecodehero | ERP System Project | n/a |
Weakness: CWE-89 · Vector: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:L
References
- https://s2.loli.net/2022/09/02/N4FESXldmKWvQOw.png x_refsource_MISC
- https://vuldb.com/?id.207845 x_refsource_MISC