Vulnerability · Published Aug 20, 2022 · Assigned by VulDB
CVE-2022-2909SourceCodester Simple and Nice Shopping Cart Script profile.php unrestricted upload
Medium 6.3
In plain English
A medium-severity unrestricted file upload in Simple and Nice Shopping Cart Script from SourceCodester. Proof-of-concept exploit code is public. The chance it is exploited in the next 30 days is estimated at 0.9% (higher than 59% of all known vulnerabilities).
Official description
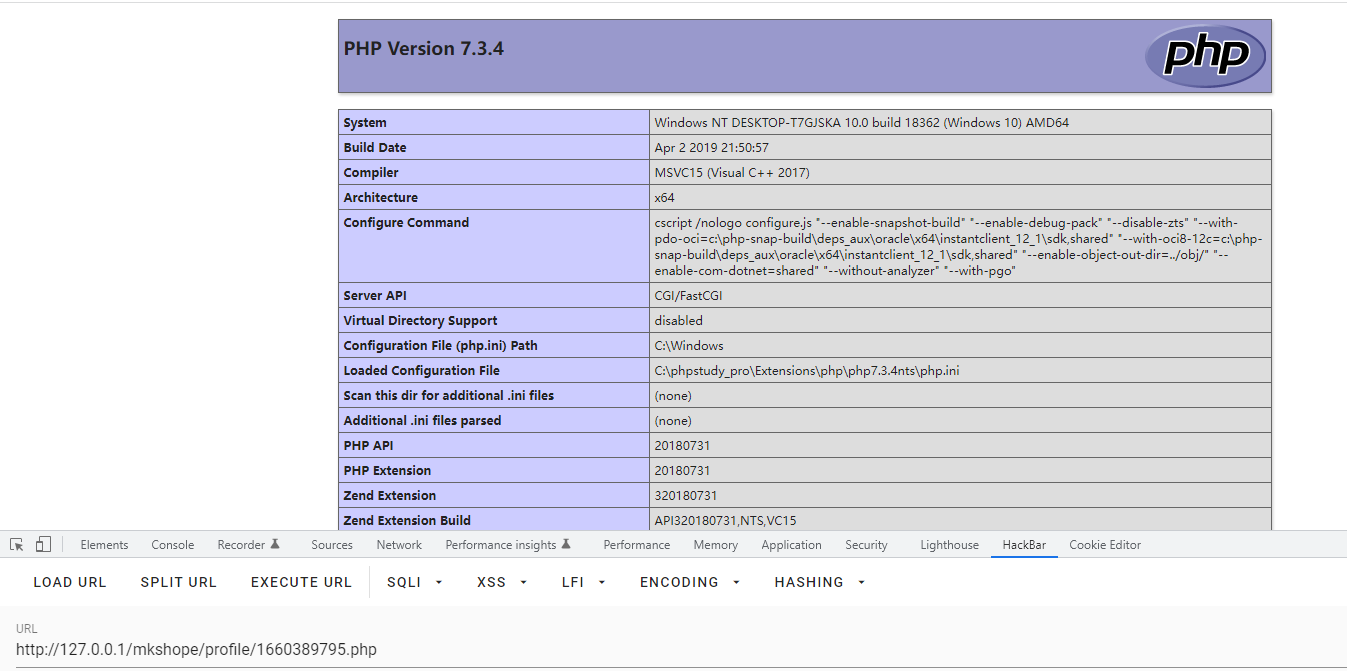
A vulnerability was found in SourceCodester Simple and Nice Shopping Cart Script. It has been declared as critical. Affected by this vulnerability is an unknown functionality of the file /mkshop/Men/profile.php. The manipulation leads to unrestricted upload. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-206845 was assigned to this vulnerability.
Affected products (as reported)
| Vendor | Product | Versions |
|---|---|---|
| SourceCodester | Simple and Nice Shopping Cart Script | n/a |
Weakness: CWE-434 · Vector: CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:L
References
- https://s1.ax1x.com/2022/08/14/vUSyHH.png x_refsource_MISC
- https://vuldb.com/?id.206845 x_refsource_MISC