Vulnerability · Published Mar 28, 2022 · Assigned by mitre
CVE-2022-23884
Critical 9.8
In plain English
A critical-severity security flaw in the affected software. There are no confirmed reports of exploitation so far. The chance it is exploited in the next 30 days is estimated at 2.6% (higher than 85% of all known vulnerabilities). Ready-made attack tooling exists: public proof-of-concept code.
Severity (CVSS NVD)9.8Critical
Exploit odds (30 days)2.6%top 14.7% of all CVEs
Exploited in the wildNo reportsnot in CISA KEV
Attack tooling1Public PoC
Official description
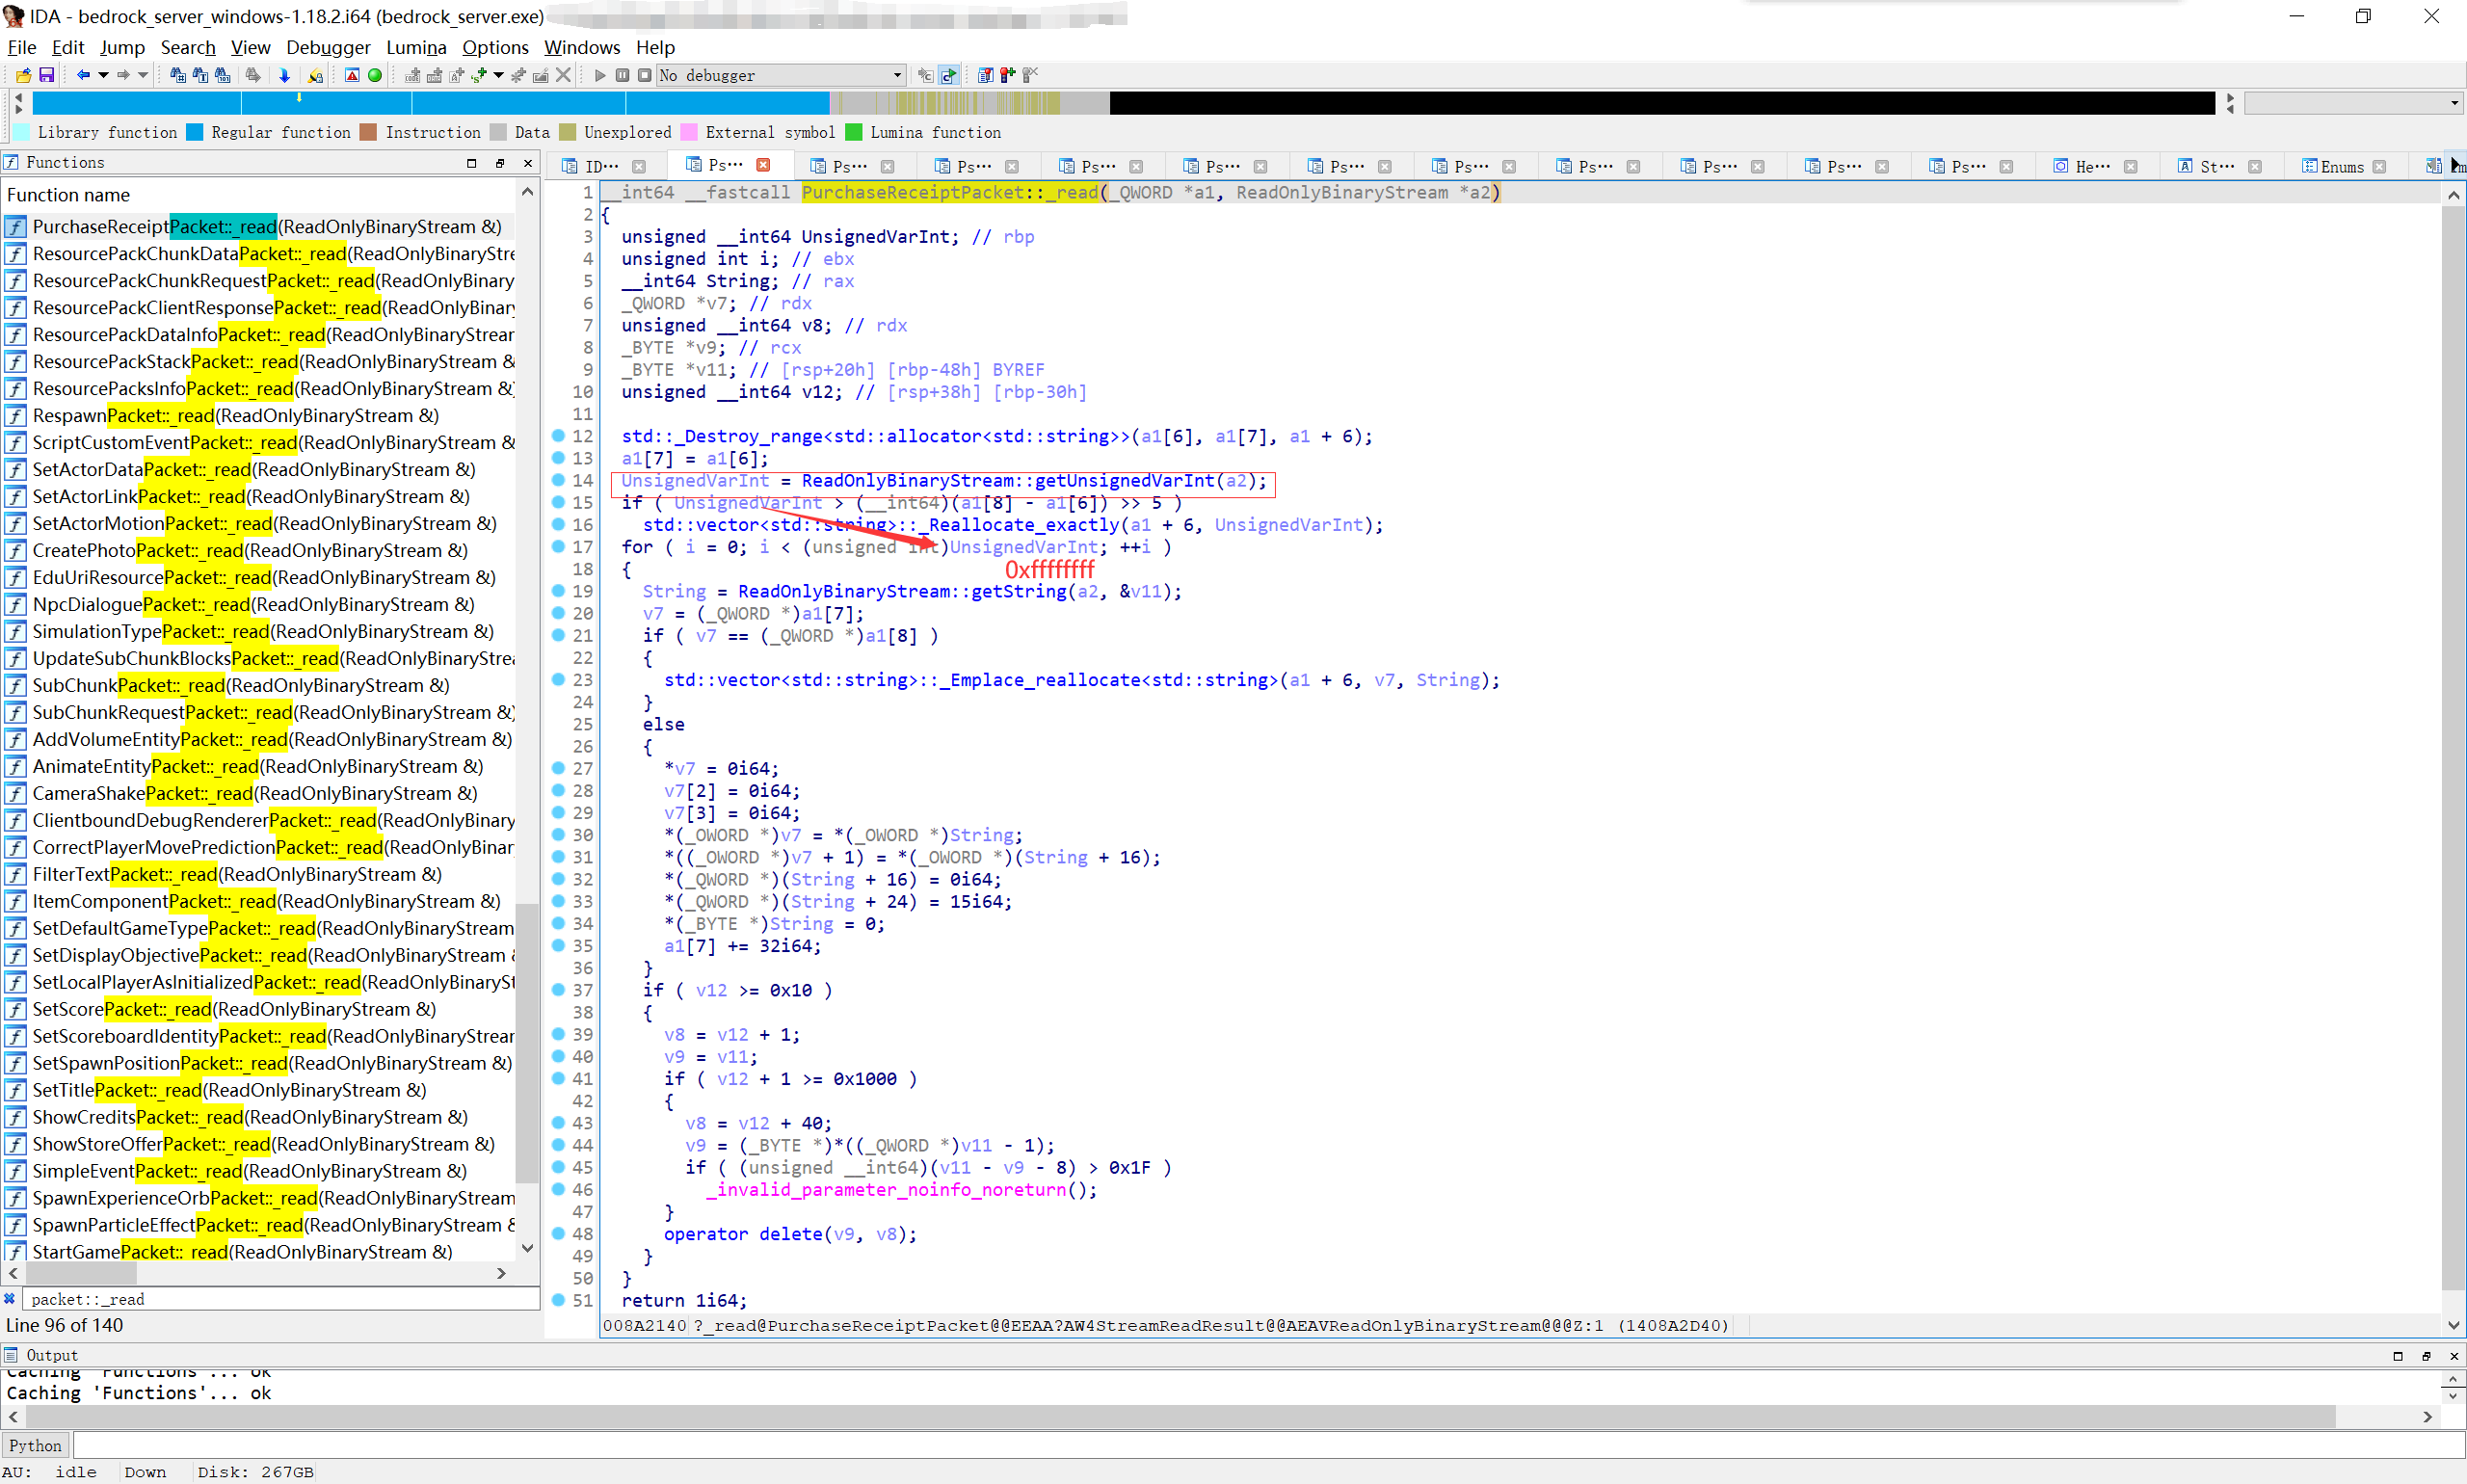
Mojang Bedrock Dedicated Server 1.18.2 is affected by an integer overflow leading to a bound check bypass caused by PurchaseReceiptPacket::_read (packet deserializer).
Affected products (as reported)
References
- https://s3.bmp.ovh/imgs/2022/01/962e0c75f5969cfb.png x_refsource_MISC